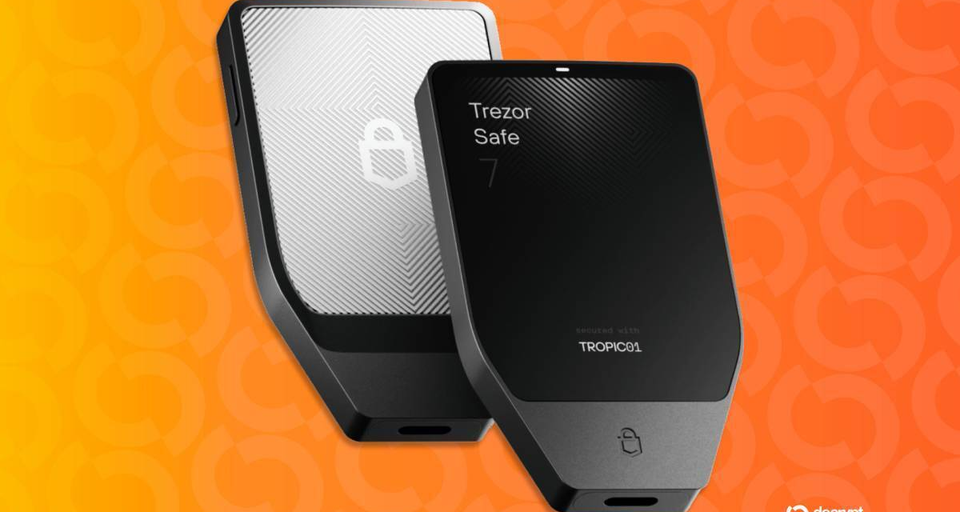

Trezor, the maker of hardware cryptocurrency wallets, has disclosed that hackers breached its email provider. The company said the incident involved a fraudulent security alert that falsely claimed a hardware flaw could expose users’ recovery phrases.
Details of the Breach
According to Trezor, the attackers gained access to its email provider and used that access to distribute a fake security alert. The alert warned recipients of a hardware vulnerability that could allegedly compromise their recovery phrases.
Recovery phrases are critical for restoring access to cryptocurrency wallets, making them a prime target for malicious actors. Trezor has not provided further specifics about the breach or the number of users affected.
Company Response
Trezor has acknowledged the breach and the fraudulent alert. The company’s statement indicates that the email provider was compromised, but no additional details about the attack or its aftermath have been released.
Users are advised to remain cautious of unsolicited security alerts and to verify any claims through official channels. Trezor has not issued any further guidance beyond confirming the incident.